
…NANI?(machines)
Elvith Ma'for
Former Reddfugee, found a new home on feddit.de. Server errors made me switch to discuss.tchncs.de. Now finally @ home on feddit.org.
Likes music, tech, programming, board games and video games. Oh… and coffee, lots of coffee!
I � Unicode!
- 2 Posts
- 279 Comments
Joined 2 years ago
Cake day: June 21st, 2024
You are not logged in. If you use a Fediverse account that is able to follow users, you can follow this user.
Good Karma Coffee is also in my rotation - nice choice. I usually try to go with small artisanal roasters and get rarely disappointed by them.
Also if you find a local roaster, you can usually stop by and talk with them about their coffee and learn and discover new things. And maybe they’ll even invite you to a tasting :)

Don’t forget that the electricity of your stove (or the gas you use) may be made of dinosaurs. So you basically burn dinosaurs to prepare a meal from their descendants pressed into a dinosaur shape

 4·25 days ago
They will be drowned in hundreds of „Thanks for your email, but we don’t do support via mail. Please open a ticket at $URL“ and „Thanks for your mail, we will get back to you shortly. Your ticket ID is #123456“. Also everything you add as an auto response will be distributed to all other victims in that group, so I chose to not be a dick.
Google Groups allows spammers to subscribe you to their groups in a workspace account, but doesn’t allow you to unsubscribe since you’re not part of that workspace account… Worse - all autoresponders for the spam will also be forwarded to all members of said group.
Since I do not participate in Google Groups, the nuclear option is to file all mails from Google Groups as spam with a Sieve script.
Note the
requirepart may be too large as may sieve script also contains more rules than this one.require ["body", "date", "editheader", "envelope", "fileinto", "imap4flags", "mailbox", "regex", "reject", "variables"]; if anyof( header :contains "List-Subscribe" "groups.google.com", header :matches "X-Google-Group-Id" "*" ) { if header :matches "Subject" "*" { set "subject" "${1}"; } else { set "subject" ""; } deleteheader "Subject"; addheader :last "Subject" "[Google-Groups-Spam] ${subject}"; fileinto "Junk"; }
 11·25 days ago
My gaming PC survived from 2021 to 2026 without “overclocked” RAM because the BIOS would just error out in the POST when I enabled DOCP to boost it from 2600 to 3200 MHz.
A Bios update this spring finally solved it. It was a nice little performance boost, but not that much as I expected. So I guess you’re fine with slower RAM.
 2·26 days ago
I use public toilets, and I piss on the seat
[ … ]
I’m an asshole !No, you’re a dick. An asshole would shit on the toilet seat…
 1·26 days ago
My current setup for this:
I own a domain - say homelab.com - and use it exclusively in my internal network.
The public DNS records do only resolve to 127.0.0.1 (as my domain holster doesn’t want me to have no A record).
In my home network I have a pihole running that resolves this domain and it’s subdomains locally (say pihole.homelab.com, proxmox.homelab.com and so on).
For HTTPs: As this server is not publicly reachable, I use the DNS API of my domain host to get a let’s encrypt certificate with the DNS-01 challenge. That way, the internal systems do not need to be exposed to the internet.
Edit: Caddy can do DNS-01, but you usually have to compile it yourself to include the plugin for your provider. To circumvent that, I’m just using plain old certbot and told Caddy to use the certs that are already on the machine
shakes fist into air
SCNR

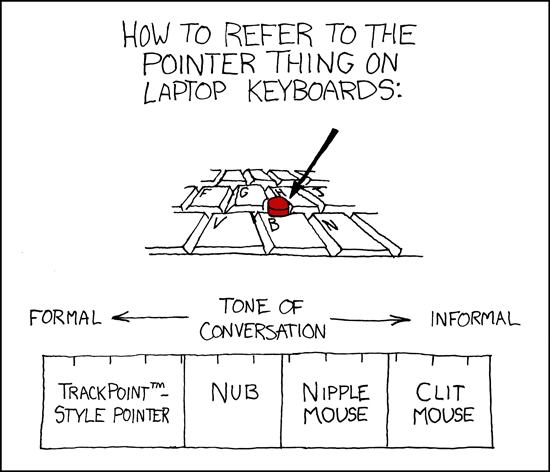
Old McDonald has a network
E I G R P
And on his network he has some traffic
E I G R P
With an ACK here and an ACK there
Here an ACK, there an ACK
ACK ACK everywhere
Old McDonald has a network
E I G R P


Not sure about this gate here, but in my company we do have gates and need to scan our company ID to enter or leave the building. If there’s a fire and the alert is on, then the gate will just automatically open up and let you out
I do not recognize the bodies in the
waterair
 1·2 months ago
Combine that with deduplicating file systems that will break fuels into chunks and if some of those are the same as another file, it will only get referenced, not stored twice. This then even works if two users upload the same file without sharing it. (Assuming files aren’t encrypted by the user)
Generally yes, but I wasn’t talking to them. If you switch operating systems, you need to do some work to learn how they work. Yes, Linix could be way more „noob friendly“. Yes, even distributions that make this process as painless as possible (e.g. Fedora that automates everything with
akmods) require you to load the generated MOK into your UEFI manually and that looks very scary (by design - it’s usually only a good idea to load a MOK if you know what you’re doing and why as it can break the whole trust concept of secure boot).The main problem with Linux for mass adoption is IMHO that there’s still many cases that require you to leverage the terminal or edit config files. And to some degree that there isn’t „one official way“ of doing or customizing things. Yes it’s cool to be able to do all those things and to have the freedom, but I also respect people that just want it to work and not need to tinker everywhere.
I feel there’s a trust problem here. I’m no Windows dev, so I don’t know all the details, but since MS enforces secure boot, they have to play by the rules: Only trusted code can be executed with very high (kernel level) privileges. That’s one of the reasons why they want to enforce signed binaries. Especially for drivers and other stuff.
On Windows that means only entities that MS trusts are allowed to execute high privileged code. Otherwise you wouldn’t get your binaries signed by MS (or co-signed, or white-listed or whatever aproach they take in this scenario) and without signature, no execution. You need to trust MS, but you need to trust them anyways, as they control the chain of trust on boot and also create the very kernel you’re running on. If they wanted to cheat you, it’s be easy for them.
On Linux it’s a bit different. Linux has the aproach that any user with root privileges is trustworthy. That’s good for me, as I get a say on what runs on my hardware and how it runs. But for the anti cheat vendor that’s now a huge problem, because a random person is now the one controlling the kernel, its integrity and the chain of trust on boot. Worse: It’s usually the very person they’re trying to observe if they’re cheating. But how do you do this, if they (theoretically) have full control over the kernel and can run arbitrary kernel modules?
Now, I’m not saying that there’s no trust in the Linux kernel and Windows were more secure - just that there are completely different assumptions about trust and trust boundaries that may lead to severe headaches for the anti cheat vendors.
How does DKMS and such break secure boot? If you want to load (custom) kernel modules, just generate a key pair, sign the module yourself, import your MOK into your UEFI (once, assuming you use the same key for all your modules and also keep a backup of your reinstall your system) and secure boot will let you do that.
I’m running current NVIDIA drivers on Linux and that’s basically the setup to use them- and since that is already set up, i’d not even need to to anything specific to get it working for other things.
Note: I do not endorse kernel level anti cheat and would never load such a module, but the infrastructure for it is already there and can be used with secure boot…

7