
112·
10 days ago
In theory yes, in practice, I have no idea. My guess is you would need to soft-fork the project to get it using either project, or maybe be really, really nice to the devs and ask them to support additional protocols. Technically there is no reason it wouldn’t work, but whether or not there are enough people with your usecase for devs to justify implementing a new feature is another matter entirely.
From what I can tell, the issue with Wireguard is that the traffic is quite obvious. Other options might be blocked, but technically harder to implement said blocks.
Yeah, WG is by far the best way to do this kind of networking.
That’s quite fascinating, didn’t realize Wireguard could be blocked in that way (although the WG traffic is pretty obvious looking, so it makes sense). The only solution I know of without a need for a VPS is hosting everything on Tor. Wildly private and secure, but also wildly slow. Beyond that, there are a number of ways of using a VPS to similar effect, I know people have used Cloudflare Tunnel to similar effect in the past.
Also, there are apparently quite a number of wiregaurd derivatives which protect better against detection and blocking methods. amnezia and wstunnel are the two that came up. Likewise, you will need a VPS, and might even be able to set up a tailscale-like coordination server that way (maybe with headscale, or maybe with one of its competitors like NetBird).
ZeroTier might also get the job done, but I really don’t know much about it.
Hope this helps, and good lucks!
The best number.
This is a very apt description of it. I remember the creation of Arda, but beyond that, it’s all a bit fuzzy, like I read the Wikipedia page half asleep and dreamed the rest.
Anyone have a link to download Control Tower Simulator X? Asking for a friend.
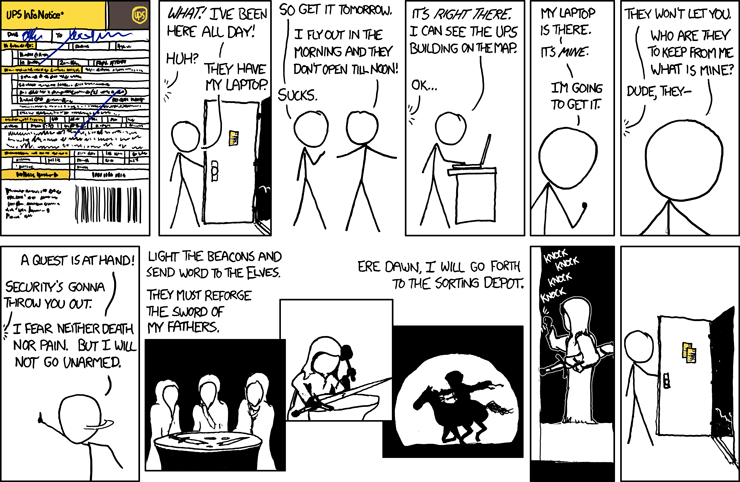
Send word to the elves! the time has come. The sword of your forefathers must be reforged! You have my bow. Err the break of dawn, we ride!
I guess they read the silmarillion, but understood not the words they read.

Listened to a rather interesting episode of Darknet Diaries the other day about a European cyber crime group. To this day, the FBI has been unable to decrypt the devices. The feds didn’t give too many details about the specifics, but what they did share was quite interesting:
From what I gathered, I think the optimal balance of usability and security (especially for a headless machine) would be the following:
It is also very much worth noting, even though the FBI never got into the hackers’ computers, they had more than enough evidence to convict the lot. Being the defender of a computer system is always a losing battle.
I will legitimately go esc, :w, i on Google Docs to try and save the document…
I am in this picture… I don’t know if I like it or not, but I am in it.